 Code of Conduct
 Ethical Mgmt
 Speak-up Culture
 Latin America
 Asia Pacific
 FX Global Code
 Financial Services
 North America
 Europe
 Middle East
 MSBs
 FinTech
 Insurance
 Investing
 Casinos
 Retail Banks
 Manufacturing
 U.S. National
 Canada
 California
 New York
 Illinois
 Connecticut
 Maine
 Delaware
 Retail
 Warehouse
 Healthcare
 Animated
 Billing & Revenue
 IT & Admins
 Leadership
 Ontario
 British Columbia
 UK Induction
 Australia & NZ
 Workplace Violence Prevention
 Canada
 Italy
 Active Shooter
 AI & Workplace
 Corporate Ethics
 Whistleblower
 Gvmt Contracting
 Export Controls
Your phishing campaign results tell you who fell for it. They say nothing about the employee who smelled something fishy, hit the report button, and got on with their day.
That employee is the whole point of security awareness training. Meet Reporter, the newest part of Phishing Defense, built to give them the credit they've earned.
Report from the inbox, get credit in the dashboard
When an employee reports a simulated phishing email using the report button already built into Gmail and Outlook, Ethena catches it, and that report shows up in your admin portal.
On a recent demo, an IT leader asked us: "So you get a specific phish button for Ethena, as opposed to the regular Google one?" Nope, and that's the point. The regular one is the button that counts. Nothing for employees to install. Nothing new for them to learn.
A new Flagged status appears alongside delivered, opened, and clicked, per campaign and per employee, so you can report on the positive behavior instead of just the slip-ups.
The behavior you're actually trying to build
Nobody runs phishing tests to catch employees clicking. You run them to build a workforce that pauses, checks the sender, and reports what looks off. Until now, that instinct was invisible in your results: an employee who reported your test email looked exactly like one who ignored it.
It's the ask we kept hearing from IT leaders, almost verbatim: "Is there a way to see that someone saw it, didn't click on it, and actually reported it?" Now there is. Reporter makes the right behavior measurable, your next security review gets a new stat worth sharing, and your most vigilant employees stop being a rounding error.
Click data you can trust
If your security stack pre-scans links, you've probably had "clicks" that were really a scanner doing its job, inflating your failure rates and making results hard to defend. Phishing Defense now screens out scanner pre-loads, so click rates reflect materially more of what humans actually did.
Part of Phishing Defense
Reporter joins a phishing toolkit that already works hard:
- Realistic tests, minus the busywork: Simulator builds campaigns from 100+ real-world templates with randomized, staggered delivery, so your cover isn't blown by everyone getting the same email at once.
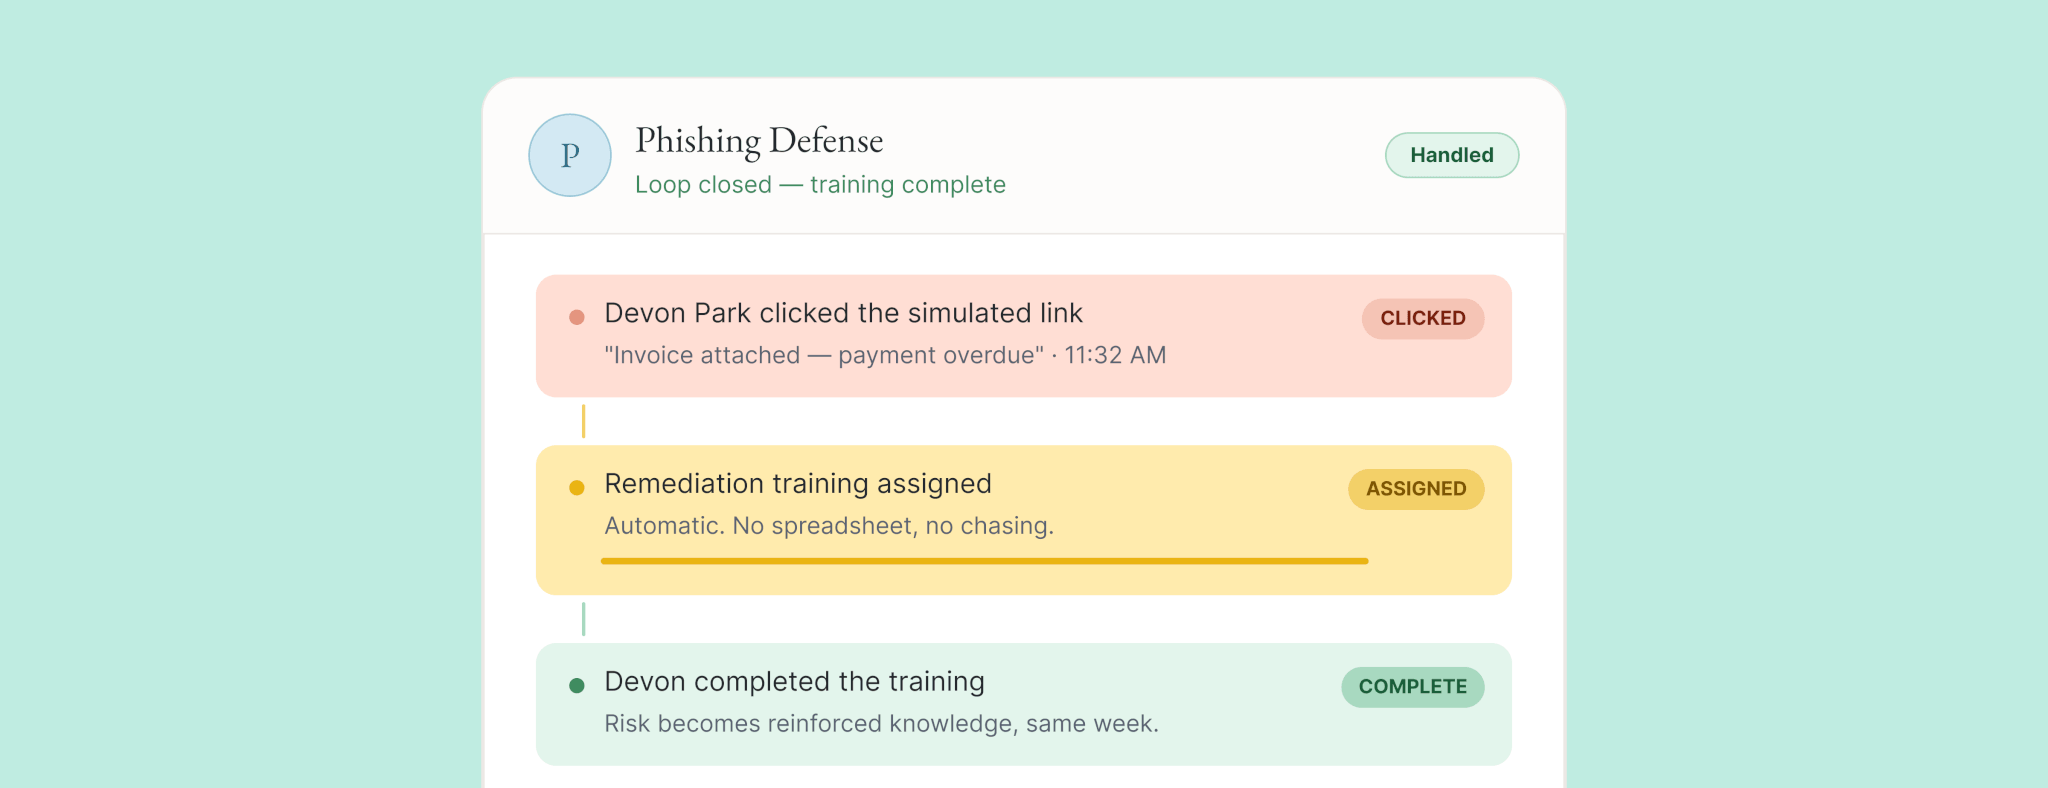
- Failure becomes a teachable moment: employees who click get remediation training assigned automatically.
- One platform, one roster: phishing lives alongside all your compliance training, including Cybersecurity Awareness. No separate tool, no separate employee list, one dashboard.
Setup is a one-time IT task
Your IT team connects your Google Workspace or Microsoft 365 email to Ethena once. After that, reporting flows in on its own.
Give your employees credit
Reporter is live now for Ethena Phishing customers. Not running Phishing Defense yet? Let's talk.